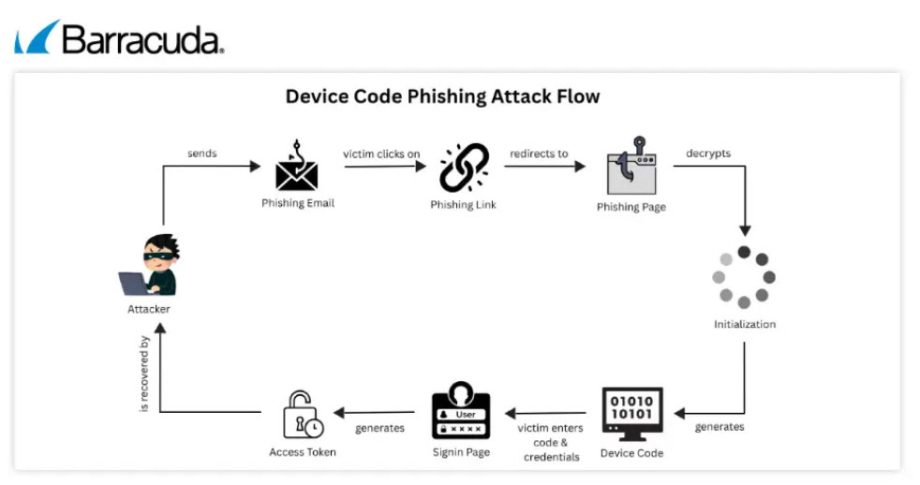
A New Phishing Tactic Is Bypassing Passwords — and Why Small Businesses Should Pay Attention
Cybersecurity threats continue to evolve, but recent findings from Barracuda Networks highlight a significant shift in how phishing attacks are carried out. In April 2026, Barracuda reported detecting more than 7 million device code phishing attacks in just four weeks, linking the surge to a phishing‑as‑a‑service kit known as EvilTokens. These attacks specifically target Microsoft […]

Cybercriminals Are Now Targeting VPN Users Through Fake Downloads — What SMEs Need to Know
Cybersecurity threats are evolving fast, and recent evidence shows that attackers are getting smarter at impersonating trusted software to steal credentials. A new campaign identified by Microsoft reveals how a threat actor known as Storm‑2561 has been tricking people into downloading fake VPN software — a tactic that puts businesses of all sizes at risk, […]
AI Adoption Is Not a Race. Maturity Matters.
Artificial Intelligence (AI) continues to dominate technology and cybersecurity discussions. Headlines often focus on two extremes: stories about AI-related security failures and concerns about data exposure, or success stories where organisations achieve impressive productivity gains through AI adoption. As AI capabilities continue to evolve, many organisations are exploring how AI can support research, automate repetitive […]
AI-Assisted Discovery of PHP Vulnerabilities Highlights Growing Cyber Risks
Date: 23 October 2026 Prepared by: Cyber Safe Business (CSB) Cyber Security Alert Cybersecurity researchers have reported that artificial intelligence assisted in identifying previously unknown vulnerabilities within PHP, one of the world’s most widely used web application technologies. The discovery prompted organisations and government agencies around the world to assess whether their systems may be exposed […]
Understanding the Shift to Software‑Defined Automation — And What It Means for Cybersecurity in SMEs
Schneider Electric’s launch of EcoStruxure Foxboro Software‑Defined Automation (SDA) marks a major shift in how industries manage technology and control systems. The system decouples software from hardware, adds stronger security controls, and moves toward open, interoperable platforms that can evolve without constant hardware upgrades. While this is an industrial product, the underlying message is relevant […]
Agentic AI: The New Workforce — And the Identity Gap Businesses Must Address
Artificial intelligence is accelerating into a new phase. Beyond chatbots and automation, organisations are introducing agentic AI — autonomous systems capable of taking action, accessing data, and interacting with business systems much like human employees. This shift brings significant efficiency, but also a major security concern:Most AI agents currently operate with no formal identity, lifecycle management, or […]
Two Recent Incidents, One Clear Message: Cyber Resilience Matters
Recent reports from the United States highlight two very different cyber incidents — one affecting a major healthcare provider, the other involving a global financial platform. While the industries differ, the underlying lesson is the same: cyber risk is no longer theoretical. It directly impacts operations, customers, and trust. At CSB, we believe these cases […]
Malvertising Campaign Targets Mac Users Through Hijacked Google Ads Accounts
We recently reviewed research from Bitdefender highlighting an active malvertising campaign targeting macOS users. The findings show how attackers are increasingly abusing legitimate advertising platforms to distribute malware — without exploiting any software vulnerability. Instead, they are exploiting trust. According to Bitdefender, threat actors hijacked legitimate Google Ads accounts to deliver malicious sponsored results to […]
Strengthening Superannuation Security: Why Phishing-Resistant Authentication Can No Longer Wait
We recently reviewed an article from SecurityBrief covering the 2025 superannuation cyber incidents, along with updates relating to APRA’s CPS 230 operational risk standard. We believe this is an important topic for our audience, particularly as it highlights how credential theft continues to put Australians’ retirement savings at risk. With cyber threats evolving and regulatory […]
Android Malware “PromptSpy” Uses Generative AI to Stay Hidden on Devices
We recently reviewed new research from ESET, which has identified an Android malware family dubbed PromptSpy. According to ESET researcher Lukáš Štefanko, this appears to be the first observed Android malware sample using generative AI to maintain persistence on infected devices. The discovery is notable not because AI is controlling the entire attack, but because […]